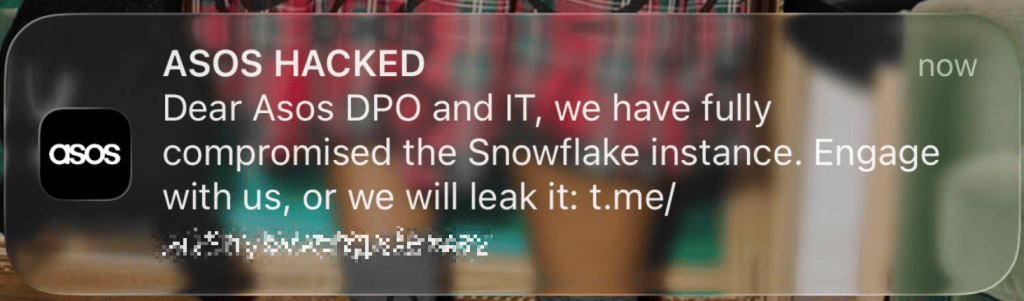
Thousands of global fashion retailer ASOS customers have received a push notification through the ASOS app this morning alleging that the company has been hacked.
The notification, addressed to ASOS’s data protection officer and IT, says:
“ASOS HACKED
Dear Asos DPO and IT, we have fully compromised the Snowflake instance. Engage with us, or we will leak it”
What we know so far
Snowflake is a cloud-based data platform that organizations use to store, process, and analyze data. We know that ASOS’s marketing team uses Simon AI from a blog posted by Simon. Simon AI specializes in personalization and runs on Snowflake. ASOS has described using Simon AI alongside Braze to personalize and trigger customer communications like push notifications to clients’ phones.
The apparent delivery of the message through ASOS’s own app makes this more concerning than an unsupported social-media claim. It suggests unauthorized use of the notification infrastructure, but does not confirm that the claimed Snowflake compromise occurred or that customer data was stolen.
According to Simon AI, typical customer profiles cover:
- browsing history and products viewed
- purchase history and customer value (first-time or high-value buyers)
- demographic data
- segments such as Premier status or customers who’ve stopped buying
- geolocation and local weather
If the affected systems contain these profiles, a breach could expose a detailed picture of customers’ shopping habits and preferences. However, the published description of ASOS’s marketing setup does not establish what, if anything, the attackers accessed.
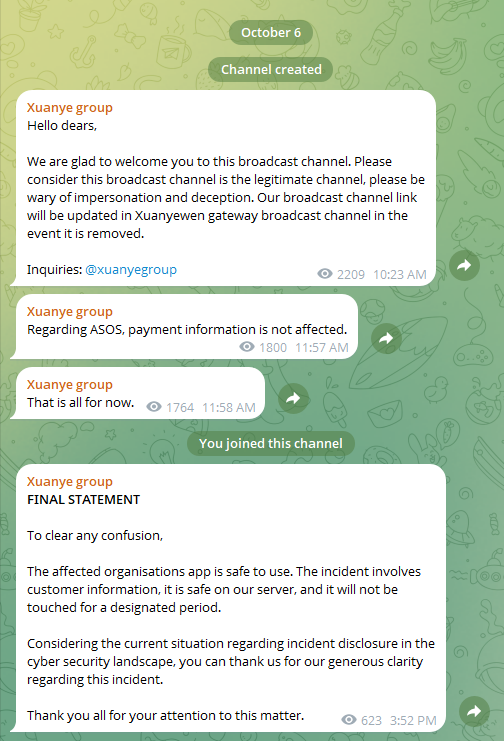
The Guardian reports that the group claiming the breach calls itself the “Xuanye group.” The Telegram channel operated by the group carried the message “Regarding Asos, payment information is not affected,” and the “app is safe to use” but those claims have not been independently verified.
Sky News reports that ASOS confirmed an “unauthorised customer notification” was sent at around 10 am today.
“We are investigating unauthorised activity involving third-party platforms that we use to communicate with customers,” it said in a statement.
The retailer said it immediately restricted access to the notification platforms and is working with specialists and relevant authorities.
It added:
“Basic personal information including name and contact details may have been accessed. We do not believe that payment-card information or account passwords, were impacted.”
How to stay safe
The website and app remain operational, and there is currently no verified evidence that customer databases, payment card information, passwords, etc. have been stolen.
So, it’s too early to say if and how much ASOS customer data the attackers could get their hands on, but the potential scope is significant. Customer data could be used in targeted phishing attacks to add credibility.
- For the time being, postpone your purchases at ASOS until it’s clear what happened and whether ASOS has resolved the issue.
- Be wary of unsolicited messaging about the breach or other ASOS related issues.
- If you do not wish to see more push notifications from the Xuanye group, remove the ASOS app until their access has been removed.
- If it turns out your data was stolen in this breach, read the tips in our blog Involved in a data breach? Here’s what you need to know.
What do cybercriminals know about you?
Use Malwarebytes’ free Digital Footprint scan to see whether your personal information has been exposed online.