

Extortion group ShinyHunters is not afraid to make enemies. Now it claims to have breached the FBI.
After reportedly taking over ransomware group Clop’s leak site, ShinyHunters says it attacked the FBI to punish the agency for spreading what it calls false information about the group.
In a very long post on its leak site, the group outlines its grievances:
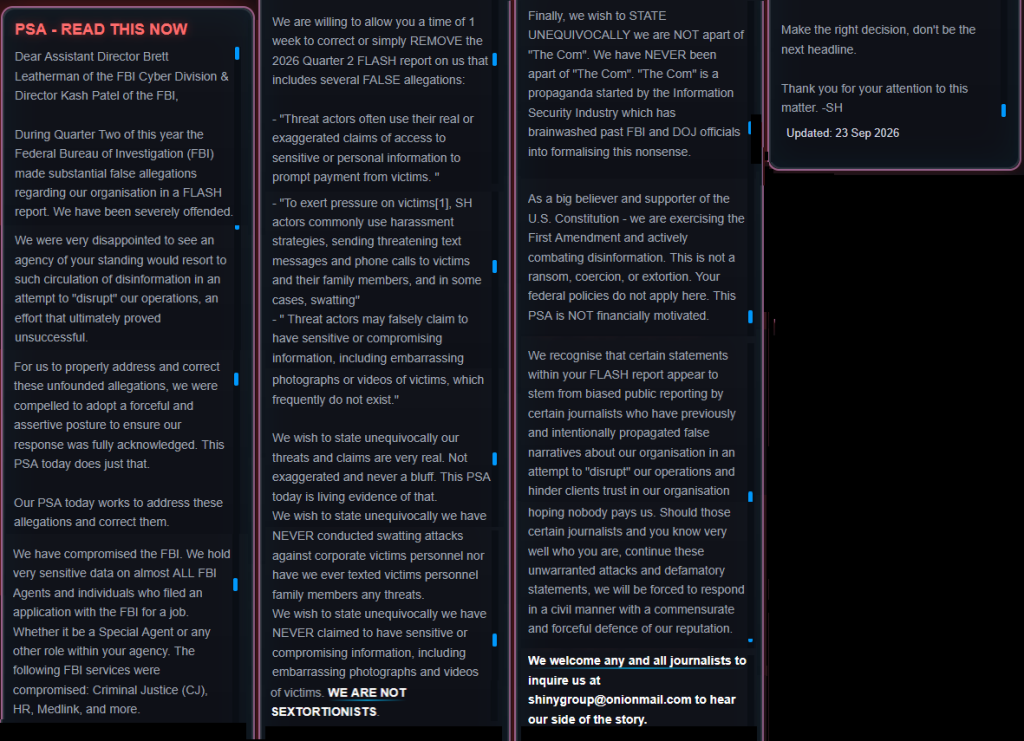
“PSA – READ THIS NOW
Dear Assistant Director Brett Leatherman of the FBI Cyber Division & Director Kash Patel of the FBI,
During Quarter Two of this year the Federal Bureau of Investigation (FBI) made substantial false allegations regarding our organisation in a FLASH report. We have been severely offended.
We were very disappointed to see an agency of your standing would resort to such circulation of disinformation in an attempt to “disrupt” our operations, an effort that ultimately proved unsuccessful.
For us to properly address and correct these unfounded allegations, we were compelled to adopt a forceful and assertive posture to ensure our response was fully acknowledged. This PSA today does just that.
Our PSA today works to address these allegations and correct them.
We have compromised the FBI. We hold very sensitive data on almost ALL FBI Agents and individuals who filed an application with the FBI for a job. Whether it be a Special Agent or any other role within your agency. The following FBI services were compromised: Criminal Justice (CJ), HR, Medlink, and more.
We are willing to allow you a time of 1 week to correct or simply REMOVE the 2026 Quarter 2 FLASH report on us that includes several FALSE allegations:
- “Threat actors often use their real or exaggerated claims of access to sensitive or personal information to prompt payment from victims.”
- “To exert pressure on victims[1], SH actors commonly use harassment strategies, sending threatening text messages and phone calls to victims and their family members, and in some cases, swatting”
- “Threat actors may falsely claim to have sensitive or compromising information, including embarrassing photographs or videos of victims, which frequently do not exist.”
We wish to state unequivocally our threats and claims are very real. Not exaggerated and never a bluff. This PSA today is living evidence of that.
We wish to state unequivocally we have NEVER conducted swatting attacks against corporate victims personnel nor have we ever texted victims personnel family members any threats.
We wish to state unequivocally we have NEVER claimed to have sensitive or compromising information, including embarrassing photographs and videos of victims. WE ARE NOT SEXTORTIONISTS.
Finally, we wish to STATE UNEQUIVOCALLY we are NOT apart of “The Com”. We have NEVER been apart of “The Com”. “The Com” is a propaganda started by the Information Security Industry which has brainwashed past FBI and DOJ officials into formalising this nonsense.
As a big believer and supporter of the U.S. Constitution – we are exercising the First Amendment and actively combating disinformation. This is not a ransom, coercion, or extortion. Your federal policies do not apply here. This PSA is NOT financially motivated.
We recognise that certain statements within your FLASH report appear to stem from biased public reporting by certain journalists who have previously and intentionally propagated false narratives about our organisation in an attempt to “disrupt” our operations and hinder clients trust in our organisation hoping nobody pays us. Should those certain journalists and you know very well who you are, continue these unwarranted attacks and defamatory statements, we will be forced to respond in a civil manner with a commensurate and forceful defence of our reputation.
We welcome any and all journalists to inquire us at shinygroup@onionmail[.]com to hear our side of the story.
Make the right decision, don’t be the next headline.
Thank you for your attention to this matter. -SH
Updated: 23 Sep 2026“
The post is essentially a hostile “correction notice” directed at FBI leaders Brett Leatherman and Kash Patel. Its central grievance is an FBI advisory that says ShinyHunters commonly harasses victims and their families, including through threatening messages, phone calls, and, in some cases, swatting.
It also warns that threat actors may exaggerate their access to personal information or falsely claim to possess compromising photos or videos. The advisory does not use the word “sextortion,” but ShinyHunters appears to have interpreted the reference to compromising material that way. The group denies much of the FBI’s account while simultaneously using coercive language of its own.
The document it appears to mean is the FBI/IC3 public advisory “ShinyHunters: Cyber Criminal Group Attacks Learning Management System,” issued on May 15, 2026. Despite ShinyHunters calling it a “2026 Quarter 2 FLASH report,” the publicly accessible document is labeled a Public Service Announcement (PSA), not a FLASH.
The picture may have been further confused by a sextortionist who pretended to be ShinyHunters. ShinyHunters declares:
“WE ARE NOT SEXTORTIONISTS.”
It also denies carrying out swatting attacks or sending threatening messages to the family members of people working for its corporate victims.
The group also denies being part of The Com, a decentralized network linked to cybercrime and violence. It calls that connection:
“propaganda started by the Information Security Industry which has brainwashed past FBI and DOJ officials into formalizing this nonsense.”
The group then threatens journalists it accuses of spreading these “false narratives.”
The most worrying part of the message is the group’s claim that it stole sensitive data on:
“almost ALL FBI Agents, and individuals who filed an application with the FBI for a job.”
According to 404 Media, ShinyHunters provided a sample containing information on roughly 5,000 FBI agents, including names, home addresses, phone numbers, and details about their spouses. The publication reportedly verified portions of the sample, but the full dataset and the wider claims about the breach have not been independently confirmed.
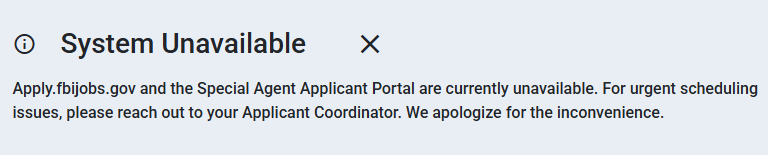
The group also reportedly defaced the FBI’s jobs website. The FBI says it is aware of claims involving unauthorized activity affecting FBIjobs.gov and is investigating, although “broken” does not necessarily mean “breached.”
What to do if you’re affected
The FBI has not yet confirmed what information was accessed or who was affected. If you are a current or former FBI employee, a relative of one, or have applied for an FBI job:
- Check the FBI’s advice. Every breach is different, so check FBI.gov for updates and follow any specific advice it offers.
- Change your password. If you have an FBI Jobs account and reuse its password elsewhere, change it on those other accounts. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
- Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop, or phone as your second factor. Some forms of 2FA can be phished just as easily as a password, but 2FA that relies on a FIDO2 device can’t be phished.
- Watch out for impersonators. Cybercriminals may contact you posing as the FBI, another government agency, or someone you know. Verify the identity of anyone who contacts you.
- Take your time. Phishing attacks often impersonate people or brands you know and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
- Set up identity monitoring. This can alert you if your personal information is found being traded illegally online and help you recover afterward.
Let’s face it, an incognito window can only do so much.
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance.








