On October 13 and 14, Google issued several Chrome updates.
Most users are on Chrome’s Stable channel. The desktop update brings Chrome to versions 155.0.8059.79/.80 for Windows and Mac and 155.0.8059.79 for Linux. The update includes 37 security fixes, including seven rated Critical.
On the same day, Google released version 155.0.8059.79 for Android. It may not be available on Google Play for everyone yet but keep an eye out for it. Google says it also includes stability and performance improvements.
Updates will roll out over the coming days and weeks.
How to update Chrome
The easiest option is to allow Chrome to update automatically. But you can end up lagging behind on updates if you never close your browser or if something goes wrong, such as an extension preventing the update.
If you don’t want to wait for the rollout to reach you, manually updating is easy. Open About Google Chrome from Chrome’s settings or Help menu. Chrome will check for updates. If one is available, click Relaunch to apply it.
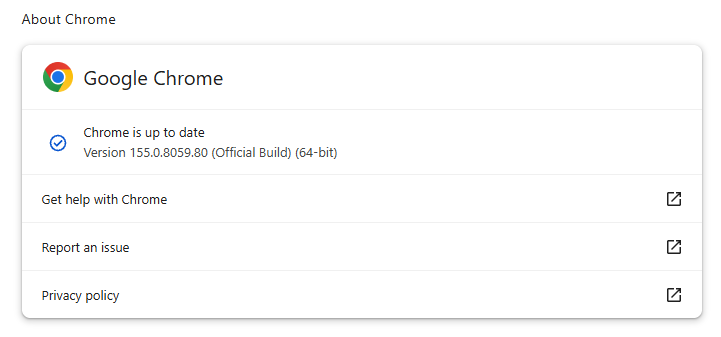
You can find an explanation of the version numbering system and step-by-step instructions in our guide: How to update Chrome on every operating system.
Technical details
Some of the security fixes deserve a closer look.
Mobile protection, anywhere, anytime.
The first is tracked as CVE-2026-110152, a buffer overflow in ANGLE in Google Chrome on Android. It could allow a remote attacker to execute arbitrary code outside the sandbox via a crafted HTML page.
ANGLE is Chrome’s graphics-translation layer. A buffer overflow occurs when a program puts more data into an area of memory than it can hold, overwriting data in adjoining memory. An attacker can exploit this to make the vulnerable process run malicious code.
Chrome vulnerabilities that enable remote code execution outside the browser sandbox are particularly valuable to attackers because they can turn a visit to a malicious or compromised website into direct code running on the underlying operating system, often without requiring additional exploitation steps.
Then I spotted two use-after-free vulnerabilities in the PDF component. CVE-2026-110136, rated Critical, could allow a remote attacker to execute arbitrary code outside the sandbox via a crafted HTML page. CVE-2026-110147, rated High, could allow an attacker to execute arbitrary code inside the sandbox via a crafted HTML page.
A use-after-free vulnerability occurs when a program attempts to access a memory location after it has been freed. That can cause crashes or, in some cases, allow an attacker to run their own code.
Inside the sandbox means the malicious code would run in a restricted, sealed-off environment designed to limit access to the rest of your device. That limits what the attacker can do as it constrains them to the browser, lowering the impact compared with code running outside the sandbox. However, attackers often chain multiple vulnerabilities together to escape the sandbox and achieve a more serious compromise. So, the phrase describes an important security limitation, but it does not mean the vulnerability is harmless.
Stop threats before they can do any harm.
Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser →