Key takeaways
- Internet safety means protecting your personal information, accounts, and devices from scams, malware, and hackers.
- Don’t click links in unexpected emails, texts, or social media messages. If you’re not sure a link is safe, check it first with the Malwarebytes Scam Link Checker.
- Use long, unique passwords stored in a password manager, and turn on multi-factor authentication (MFA).
- Keep your operating system, apps, and router updated, and use security software that blocks threats in real time.
- Be careful on public Wi-Fi, and use a VPN to encrypt your connection.
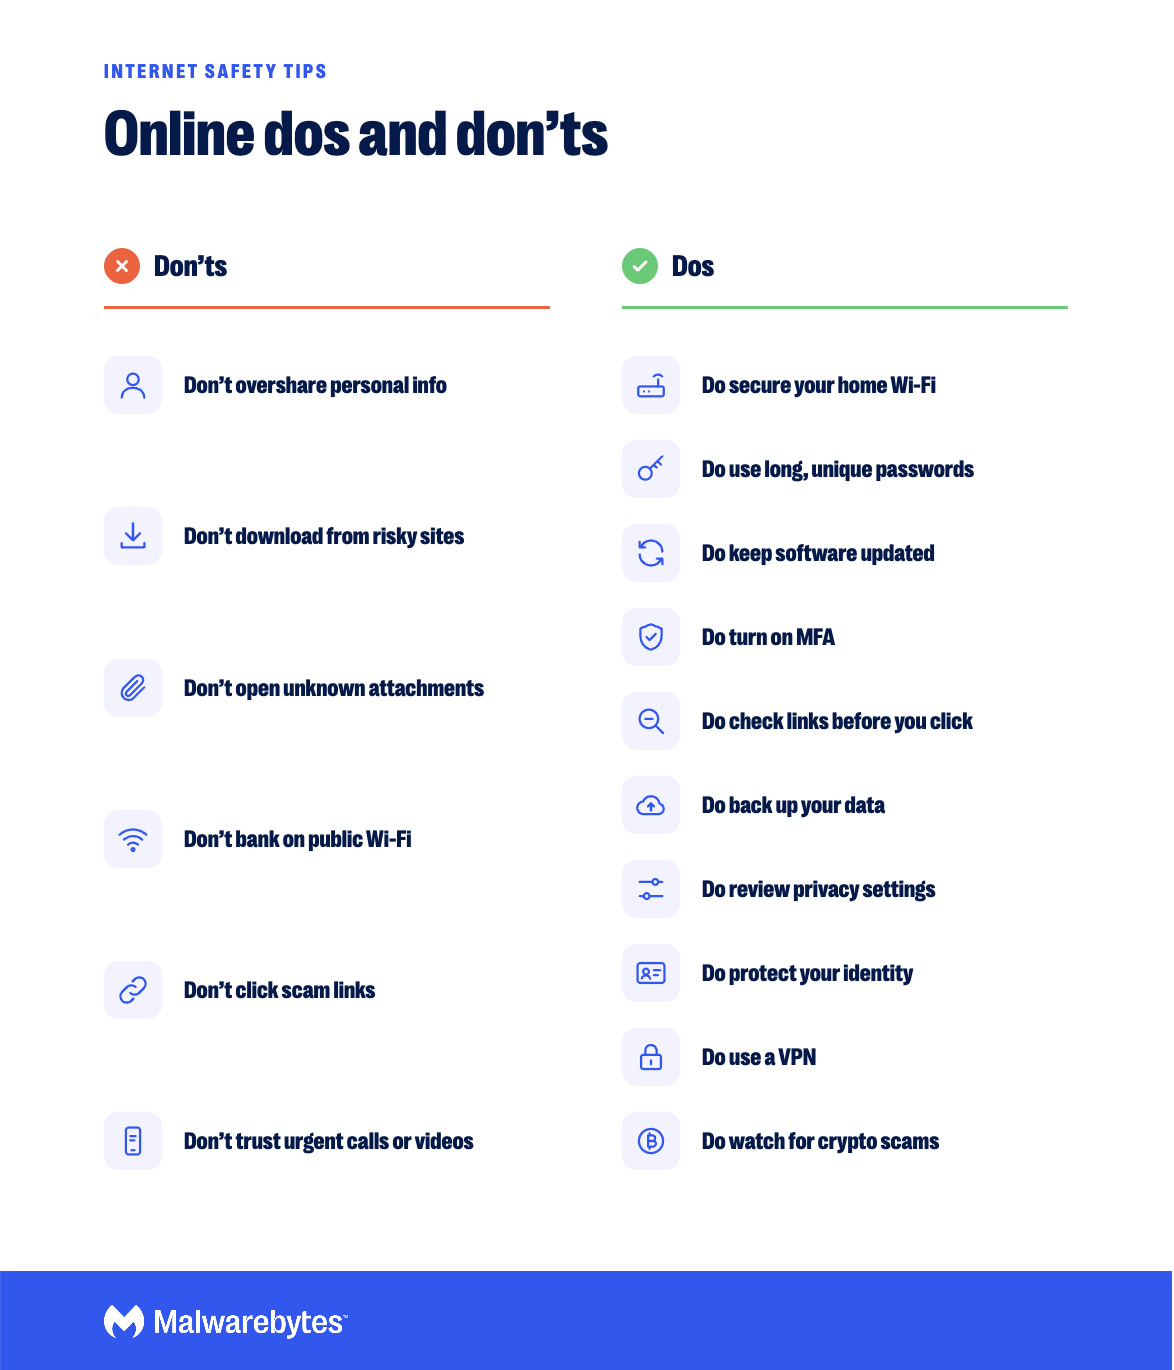
Stay safe online with these rules
Internet safety is the practice of protecting yourself, your family, and your data while you’re online. The basics are simple: share less, think before you click, use strong passwords with MFA, keep your software updated, and use security tools that block threats before they reach you.
We use the internet for shopping, banking, school, work, socializing, and entertainment, so cybercriminals have plenty of ways to reach us. The dos and don’ts below cover the habits and settings that make the biggest difference.
Don’ts of safe online behavior
1: Don’t share your personal information
One of the most overlooked internet safety tips has to do with sharing personal information. Keep details like your home address, birthday, phone number, and pet names off public profiles and forums.
We’re so comfortable online that we don’t hesitate to share personal information on message boards or social media. Vulnerable people, such as children who overshare, can be targeted by cyberbullies, predators, and doxxers.
Oversharing can also make you more susceptible to an account breach. Hackers can piece together information from public posts to craft a more convincing phishing attack. They may also use your digital footprint to get past your login security. For instance, your account could be hacked if you post about your pet on Facebook and its name matches one of your security answers.
2: Don’t download from unknown sources
Only download software and apps from official sources, such as the developer’s website, the Google Play Store, or Apple’s App Store.
Think twice before downloading unlicensed software, pirated programs, or files from untrustworthy websites and links. These downloads may carry malware such as viruses, Trojans, or spyware like keyloggers. If you think you’ve downloaded something malicious, run a free virus scan.
3: Don’t open suspicious attachments
Don’t open attachments you weren’t expecting, even if they appear to come from someone you know.
Suspicious attachments can take you to malicious websites or install malware like a macro virus or ransomware. Yet some of us still open them because we’re curious or because we’re waiting for something to arrive in our inbox.
The risk just isn’t worth it. A bad attachment can compromise your personal security and your family’s safety, and even hurt your organization.
4: Don’t do sensitive tasks on public Wi-Fi
Avoid banking, shopping, or logging in to important accounts on public Wi-Fi unless you’re using a VPN.
Public Wi-Fi at the park, mall, or airport is convenient but risky. These networks aren’t as secure as your home or office network. Threat actors may also set up fake hotspots with legitimate-sounding names to steal your data or launch a man-in-the-middle (MitM) attack.
If you have to use public Wi-Fi, stick to sites that use HTTPS, turn off automatic connections to open networks, and secure your connection with a VPN.
5: Don’t click scam links or fall for phishing
Don’t click links in unexpected messages, even if they look like they’re from your bank, a delivery company, or someone you know.
Phishing is a type of online fraud where scammers send fake emails, texts, and social media messages, or set up websites that imitate legitimate businesses. The goal is to trick you into handing over passwords, credit card numbers, or bank details, or into downloading malware such as ransomware. When the scam arrives by text message, it’s called smishing. Scammers also hide malicious links in QR codes on posters, parking meters, and fake parking tickets.
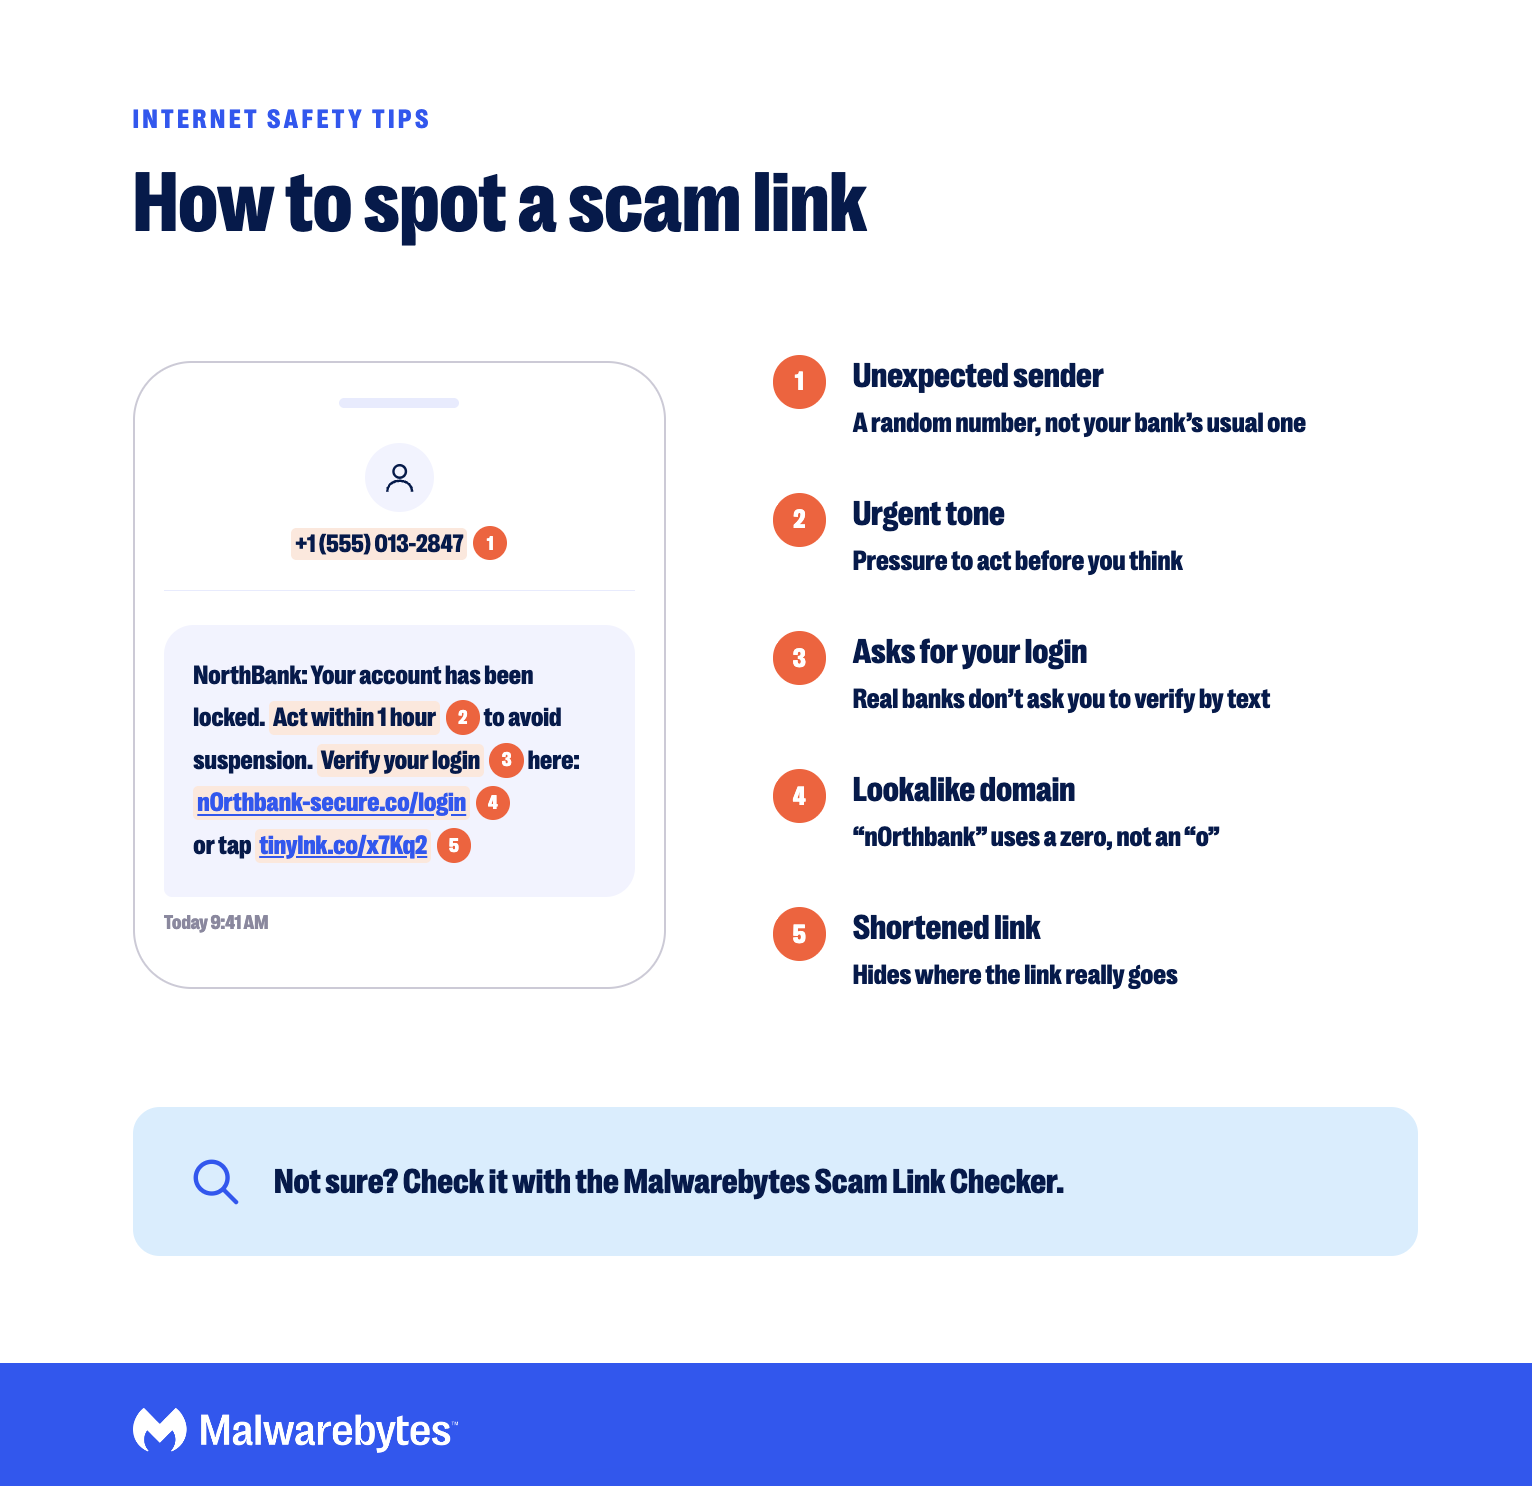
Scam links often lead to convincing fake login pages or trigger malware downloads. If you’re not sure whether a link is safe, paste it into the Malwarebytes Scam Link Checker before you open it.
If a message seems suspicious, don’t reply. Contact the company directly through its official website or app to confirm. Never share personal or financial information in response to unsolicited messages, even if they look legitimate.
6: Don’t trust a voice or video just because it seems real
Be skeptical of urgent calls, voice messages, or videos asking for money or information, even if they sound like someone you know.
Scammers now use AI to clone voices from short social media clips, generate realistic deepfake videos, and write phishing messages without the spelling mistakes that used to give them away. A common scam is a panicked call from a “family member” who needs money right away.
YEAR OVER YEAR
The “I can’t tell anymore” curve is swelling
2025
said scams were hard to spot
2026
say the same thing now
If a request feels urgent or unusual, hang up and contact the person directly using a number you already have. Some families agree on a code word for emergencies. Learn more in our report on how AI is reshaping scams.

Picked up something you shouldn’t have?
Dos of safe online behavior
1: Make sure you have a secure internet connection
A secure connection keeps unauthorized users and hackers off your network. Follow these steps to improve the safety of your home internet connection.
Turn on your firewall
A firewall is a network security system that defends your connection by controlling incoming traffic. You can turn on your operating system’s firewall and your router’s firewall too.
Turn on browser protection
A good browser security tool helps keep your browsing safe. We suggest you try Malwarebytes Browser Guard, a free browser extension that blocks unsafe content like scams and malware.

Safer. Cleaner. Ad-free browsing.
Change your default network name and admin password
Every router comes with a default network name (SSID), admin username, and password. Hackers can use the default SSID to identify your router model, look up its default login, and change its settings to break into your network.
Changing these defaults is one of the most important internet safety tips we can share. You can change both from your router’s settings. Choose a network name that doesn’t reveal your name, address, or router brand. After changing the SSID, you’ll need to reconnect your devices.
Encrypt your Wi-Fi network
In your router settings, you’ll see encryption options such as WEP, WPA, WPA2, and WPA3. Choose WPA3 if your router supports it, or WPA2 if it doesn’t. Avoid WEP and the original WPA, which are outdated and easy to crack.
Patch your router
Hackers regularly hijack home routers through known security flaws. An unpatched router is vulnerable to attacks such as remote takeover, path traversal, and botnet malware like Mirai.
Turn on automatic firmware updates if your router offers them, or check for updates regularly. If your router is no longer supported, ask your internet provider for a new one or buy your own.
2: Use strong, unique passwords
Use a long, unique password for every account, and store them in a password manager.
Why create a strong password anyway? Hackers use tools that can crack short or common passwords in seconds, and they reuse passwords stolen in data breaches to break into other accounts. That’s why one unique password per account matters so much.
Length matters more than complexity. Current NIST guidelines recommend passwords of at least 15 characters when they aren’t paired with MFA. A passphrase made of several random words is long, strong, and easier to remember than a jumble of symbols. Avoid recognizable patterns such as “ABC,” “12345,” or birthdays.
You don’t need to change strong passwords on a schedule. Do change a password right away if a service you use has a data breach or you think someone else knows it. A stolen password can have serious consequences: the Colonial Pipeline ransomware attack reportedly started with a compromised password.
A password manager makes all of this easier by generating and remembering unique passwords for you. Where sites offer passkeys, consider using them. Passkeys let you sign in with your fingerprint, face, or device PIN, and they can’t be phished like passwords.
3: Use antivirus and keep your software updated
Use security software that blocks threats in real time, and keep your operating system, browser, and apps updated.
Antivirus software protects your system from malicious software that targets your device, network, or web browser. Legacy antivirus tools may not be as effective against new and unknown threats, so choose anti-malware software that shields your browser and stops emerging threats.
Software updates bring better performance, improved compatibility, and sometimes new features. Most importantly, security updates fix vulnerabilities that hackers use to break into your hardware and software.
Make it a habit to update your operating system, web browser, phone, router, and other essential software. Turn on automatic updates for convenience.
4: Use multi-factor authentication (MFA)
Turn on MFA for every account that offers it, starting with your email, bank, and social media accounts.
Even the strongest password can be used to break into your account if it’s stolen. That’s why we recommend turning on multi-factor authentication.
With MFA, a hacker needs more than your password. Even if they have your username and password, they’ll have to prove their identity another way, such as with a code from an authenticator app or a prompt on your phone. Authenticator apps and passkeys are more secure than codes sent by text message, which can be intercepted through SIM-swap scams.
5: Check website security (HTTPS), then check the link
Before you enter personal or payment information on a website, make sure the address starts with HTTPS.
A secure URL begins with HTTPS, not HTTP. The “S” stands for secure, meaning the connection between your browser and the website is encrypted using TLS (Transport Layer Security). Many browsers flag sites that don’t use HTTPS as “Not secure.” Some browsers, including Chrome, no longer show a padlock in the address bar, so look at the URL itself.
Keep in mind that HTTPS only means your connection is encrypted. It doesn’t mean the site is legitimate. Scam websites use HTTPS too. Before shopping on a website you haven’t used before, search for reviews or reports of scams, and run the address through the Malwarebytes Scam Link Checker.
6: Back up your data
Back up your important files regularly so you can recover them after a cyberattack, device failure, or theft.
Even with the best cybersecurity tools and internet safety tips in mind, you may still suffer a breach. For example, ransomware can encrypt your files, and some malware can delete or corrupt them.
We recommend that you periodically back up your data to an external hard drive and also use a reputable cloud backup service that automatically saves your data offsite. Keeping one backup disconnected from your device helps protect it from ransomware.
7: Review your privacy settings on social media and browsers
Check the privacy settings on your browsers, devices, and social media accounts, and limit what strangers can see.
Many of us keep private information on our devices and social media platforms. Our privacy settings control who can access it. For example, your browser’s privacy settings affect what websites can see, like your browsing history or payment information.
Likewise, your privacy settings on social media platforms like Facebook, X, Instagram, and TikTok control which personal information, posts, and media strangers can access.
Use these links to update your privacy settings:
8: Protect your identity
Limit how much of your identity is visible online, and watch for signs that your information has been exposed.
Protecting your identity online lets you speak your mind without attracting the attention of cyberbullies or cybercriminals. You’re also less likely to be targeted by hackers or become a victim of identity theft.
Use anonymous handles when posting online, and combine the other internet safety tips listed here to protect your identity.
Keep an eye on your credit reports, bank statements, and credit card charges. Regularly search your name online to see what information and images are publicly available, or run a free digital footprint scan to see if your personal data has been exposed in a breach.
If you find your sensitive information published online, immediately update your privacy settings, change your passwords, and contact the platform. For ongoing protection, consider an identity theft protection service.
9: Use a VPN
Use a VPN to encrypt your internet traffic, especially on public Wi-Fi.
Securing your connection with a private VPN is one of the most essential internet safety tips. A VPN encrypts your internet traffic and masks your location, preventing hackers from intercepting your data and your internet provider from tracking your online activity. In some countries, a VPN can also help protect the privacy of citizens, activists, and journalists. Learn more in What is a VPN?
When choosing a VPN provider, pick one with a large server network, strong security features, and a no-logs policy.
Steer clear of free VPNs and free proxy servers, though. Some free VPNs are known to spy on users or sell their browsing activity to third parties like marketers. Free VPNs with weak security may also leave users vulnerable to malware.
10: Watch out for cryptocurrency scams
Never send cryptocurrency to someone you’ve only met online, and be wary of any investment that promises guaranteed returns.
Cryptocurrency scams are on the rise, and many victims have lost their life savings. Because crypto transactions are hard to reverse, victims often have few options for getting their money back.
Follow these cryptocurrency safety tips to protect your assets:
- Use a reputable cryptocurrency exchange.
- Consider storing your digital assets offline in a cold wallet.
- Protect your accounts with MFA, preferably through an authenticator app or hardware key.
- Be wary of phishing messages, fake support agents, and “investment coaches” who target your crypto.
- Ask your mobile carrier to add extra protection against SIM-swap attacks (also called SIMjacking), a common way criminals steal crypto by taking over your phone number.
What to do if you’ve been hacked
If you think a scammer or hacker has gotten into your accounts or devices, act quickly:
- Change your passwords for the affected account and any account that uses the same password, starting with your email.
- Turn on MFA for those accounts if it isn’t already on.
- Scan your devices for malware with a free virus scanner.
- Check your accounts for unfamiliar logins, purchases, or changed settings, and contact your bank if you see suspicious charges.
- Consider freezing your credit if your financial or identity information may have been exposed.
- Report it to the platform involved and, in the US, to the FTC at ReportFraud.ftc.gov.